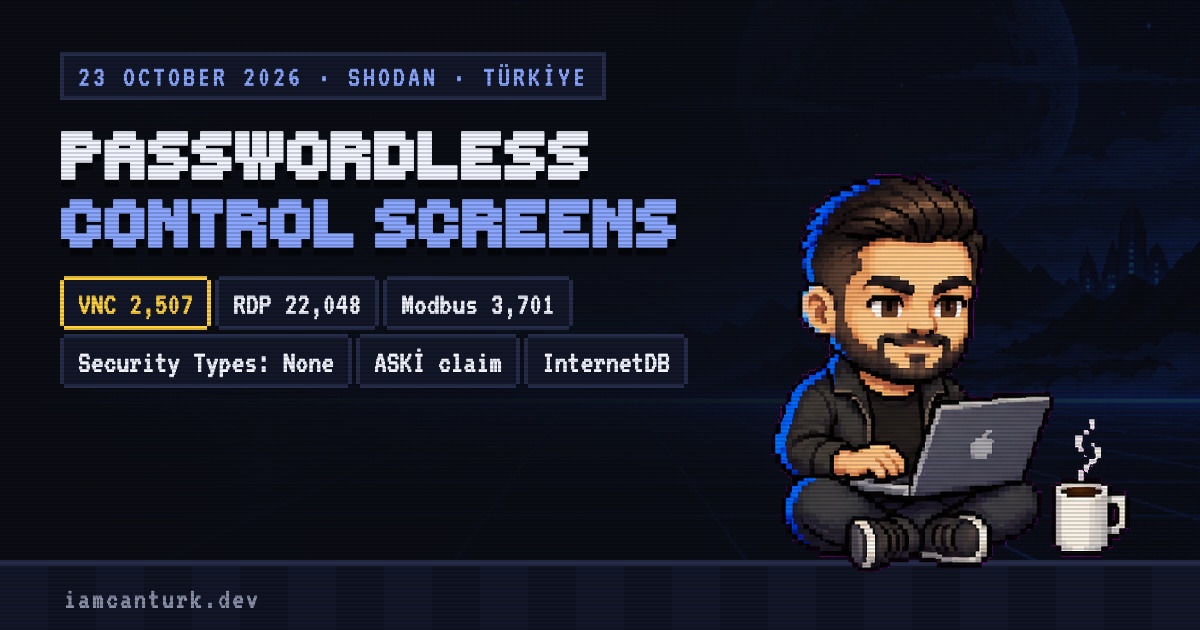
On 23 October 2026 I ran a few searches for Türkiye on my own Shodan account. Among the results were the control screens of a greenhouse, a compost room and a power plant. All three were open to the internet and asked for no password. The screenshots were taken by Shodan itself; I did not connect to any system.
This post explains what those searches show, why VNC sometimes asks for no password at all, and what the viral ASKİ claim does and doesn’t prove. Video: Pixel Shorts · Shodan sees you.
There are no IP addresses, organisation names or recognisable screens in this post. Identifiers, brands and place names in the Shodan screenshots were removed. Connecting to someone else’s system without permission is a crime even when the door is open (in Türkiye, Article 243 of the Penal Code).
At a glance
| Shodan, Türkiye, VNC (5900) | 2,507 records |
| Shodan, Türkiye, RDP (3389) | 22,048 records |
| Shodan, Türkiye, Modbus (502) | 3,701 records |
| “authentication disabled” | 774 records, mostly SMB (445); 26 on VNC (5900: 18, 5901: 8) |
| Worldwide | Forescout: ~60,000 VNC servers without authentication, 670 exposing ICS/OT panels directly |
| ASKİ claim | Unverified; ASKİ says the screens don’t match its systems |
| What to do | Keep VNC/RDP/Modbus off the internet, put remote access behind a VPN, check your IP on InternetDB |
Numbers are from the 23 October searches. Shodan counts service records, not devices; one device can have several records, and counts change daily.
What Shodan does
Shodan continuously scans internet addresses, connects to open ports and stores each server’s banner. When a VNC server asks for no password, it also stores a screenshot. All of it becomes searchable. Google indexes websites; Shodan indexes connected devices and their open doors.
The searches I used:
country:TR port:5900
country:TR port:3389
country:TR port:502
country:TR "authentication disabled"country:TRselects the country,port:the target port.- 5900/5901 is VNC: viewing and using another computer’s screen remotely.
- 3389 is RDP: Windows Remote Desktop.
- 502 is Modbus/TCP: the protocol industrial devices such as PLCs, meters and sensors speak. Modbus itself has no authentication.
Most VNC records in Türkiye sit on residential and business ISP networks: Istanbul 1,721, Bursa 141, Ankara 117, Izmir 98, Antalya 41. These are individual businesses, workshops and facilities rather than data centres.
Why VNC sometimes asks for no password
VNC uses the RFB (Remote Framebuffer) protocol (RFC 6143). After the version handshake, the server lists the security types it supports:
RFB 003.008
Security Types:
  2: VNC Authentication
1: None| Type | Meaning |
|---|---|
1: None |
No authentication. The client gets the screen straight away. |
2: VNC Authentication |
The server sends a 16-byte challenge; the client encrypts it with a DES key derived from the password. |
If the list only offers None, or the client can pick it, no password is asked. Shodan shows this as Authentication disabled in the banner. These are the lines from one VNC record I saw:
RFB 003.003
Authentication disabled
Security Types:
  1: None
Geometry: 800x480
800×480 is a typical industrial touch-panel resolution. Such HMIs often ship with an embedded VNC server; it gets enabled during installation for easy remote servicing and then forgotten along with a port forward.
VNC Authentication isn’t strong either. It relies on DES, and since a DES key is 8 bytes only the first 8 characters of the password count. Exposing VNC directly to the internet isn’t recommended even with a password.
Seeing a screen isn’t controlling it. Many VNC servers support view-only mode. Shodan’s screenshot only shows the server hands out its screen without a password; it doesn’t show whether mouse and keyboard input is accepted.
itsmelsec and the ASKİ claim
On 16 September 2026 someone using the handle “itsmelsec” published How I Hacked An Entire Country Through VNC on Substack. It spread on Turkish social media on the night of 22 October and hit the news on 23 October.
The method the author describes:
- Scanned about 17 million Turkish IP addresses on ports 5900 and 5901.
- Routed traffic through Tor, at about 300 addresses per second, for 18 hours.
- Automatically captured every VNC that asked for no password: 161 screens.
- Says they included ASKİ (Ankara’s water utility) pumps, greenhouses (with a “spray pesticide” button), a poultry farm and a prison or military site, and writes “I can turn off the water pump for an entire city”.
What is and isn’t proven:
| Claim | Status |
|---|---|
| Passwordless VNC exists in Türkiye | True; visible on Shodan too |
| 161 screenshots were taken | Author’s statement, no independent verification |
| One of the screens belongs to ASKİ | Unverified. ASKİ’s general manager Memduh Aslan Akçay said the diagrams don’t match its systems and these control screens don’t exist in its current infrastructure |
| A city’s water could be cut | No evidence; seeing a screen isn’t operating a pump |
| Organisations were notified | No disclosure timeline in the post; I found no statement from USOM (Türkiye’s national CERT) |
Two things often get mixed up:
- ASKİ’s water outage page was defaced on 4 January 2026. That’s a separate, older incident.
- The 23 October water outages in Ankara were, per local news, due to faults and maintenance. No source links them to an attack.
The method itself is questionable. Connecting to a system that asks for no password and capturing its screen can count as unlawful access to an IT system under Article 243 of the Turkish Penal Code. The right move is to report the exposure to the organisation and to USOM without connecting.
Is the problem real?
Yes. Even if the ASKİ claim is unverified, internet-exposed control panels are a documented problem:
- According to Forescout’s 2026 research (SecurityWeek, 29 April 2026), about 60,000 VNC servers worldwide have authentication disabled, and 670 of them open directly onto ICS/OT panels. The same report notes a Russia-linked group posted a VNC screenshot of a control system in Türkiye on 9 March.
- CISA and partners warned in December 2025 (AA25-343A) that pro-Russia hacktivists were reaching OT devices through minimally protected, internet-exposed VNC.
None of this needs an exploit. A port scan, a Shodan search or an open VNC is enough.
Check your own server
Shodan’s InternetDB is free and needs no key. Look up your own IP:
curl -s https://internetdb.shodan.io/$(curl -s https://api.ipify.org)The result for my own server (IP hidden):
{
  "ports": [22, 80, 443, 8443],
  "tags": ["self-signed"],
  "vulns": []
}
8443 is my server’s CloudPanel admin port. On 22 October I restricted it to two VPN addresses (ufw plus a Cloudflare WAF rule). Shodan’s record was still stale on 23 October; records can lag by days depending on scan frequency. If InternetDB shows a port, first check whether it’s actually open today:
nmap -Pn -p 5900,5901,3389,502,8443 <your-own-IP>Only scan systems you own.
What to do
- Don’t expose VNC, RDP or Modbus directly to the internet. Check port forwards on your router or firewall.
- Put remote access behind a VPN. WireGuard, OpenVPN or the vendor’s secure remote access. If you need VNC, tunnel it over SSH:
ssh -L 5900:127.0.0.1:5900 user@server. - If you can’t avoid it, restrict by IP. Allow only known addresses, as I did for my panel port:
ufw allow from <VPN-IP> to any port 8443 proto tcp. - Disable the
Nonesecurity type in VNC. Use password authentication, ideally TLS or VeNCrypt, and change the panel vendor’s default password. - Keep an inventory. Regularly check your organisation’s internet-facing ranges with InternetDB or your own scans.
- If you find an exposure, don’t log in; report it. To the organisation and the national CERT.
Sources
- itsmelsec · How I Hacked An Entire Country Through VNC (16 September 2026)
- Yeni Ankara · ASKİ security claims (23 October 2026)
- ÇözümPark · Claim of internet access to Ankara’s water infrastructure
- Ankara Masası · ASKİ website defaced (4 January 2026 incident)
- SecurityWeek · Hundreds of Internet-Facing VNC Servers Expose ICS/OT (Forescout, 29 April 2026)
- CISA · AA25-343A
- RFC 6143 · The Remote Framebuffer Protocol
- Shodan InternetDB
- Shodan searches:
country:TR port:5900,port:3389,port:502,"authentication disabled"(23 October 2026)